We look at what you run
We map your estate first — including what can’t be patched or restarted.
Halonex PQC Migration Report — what a routine database migration exposes in transit, and what post-quantum cryptography changes.
Get the report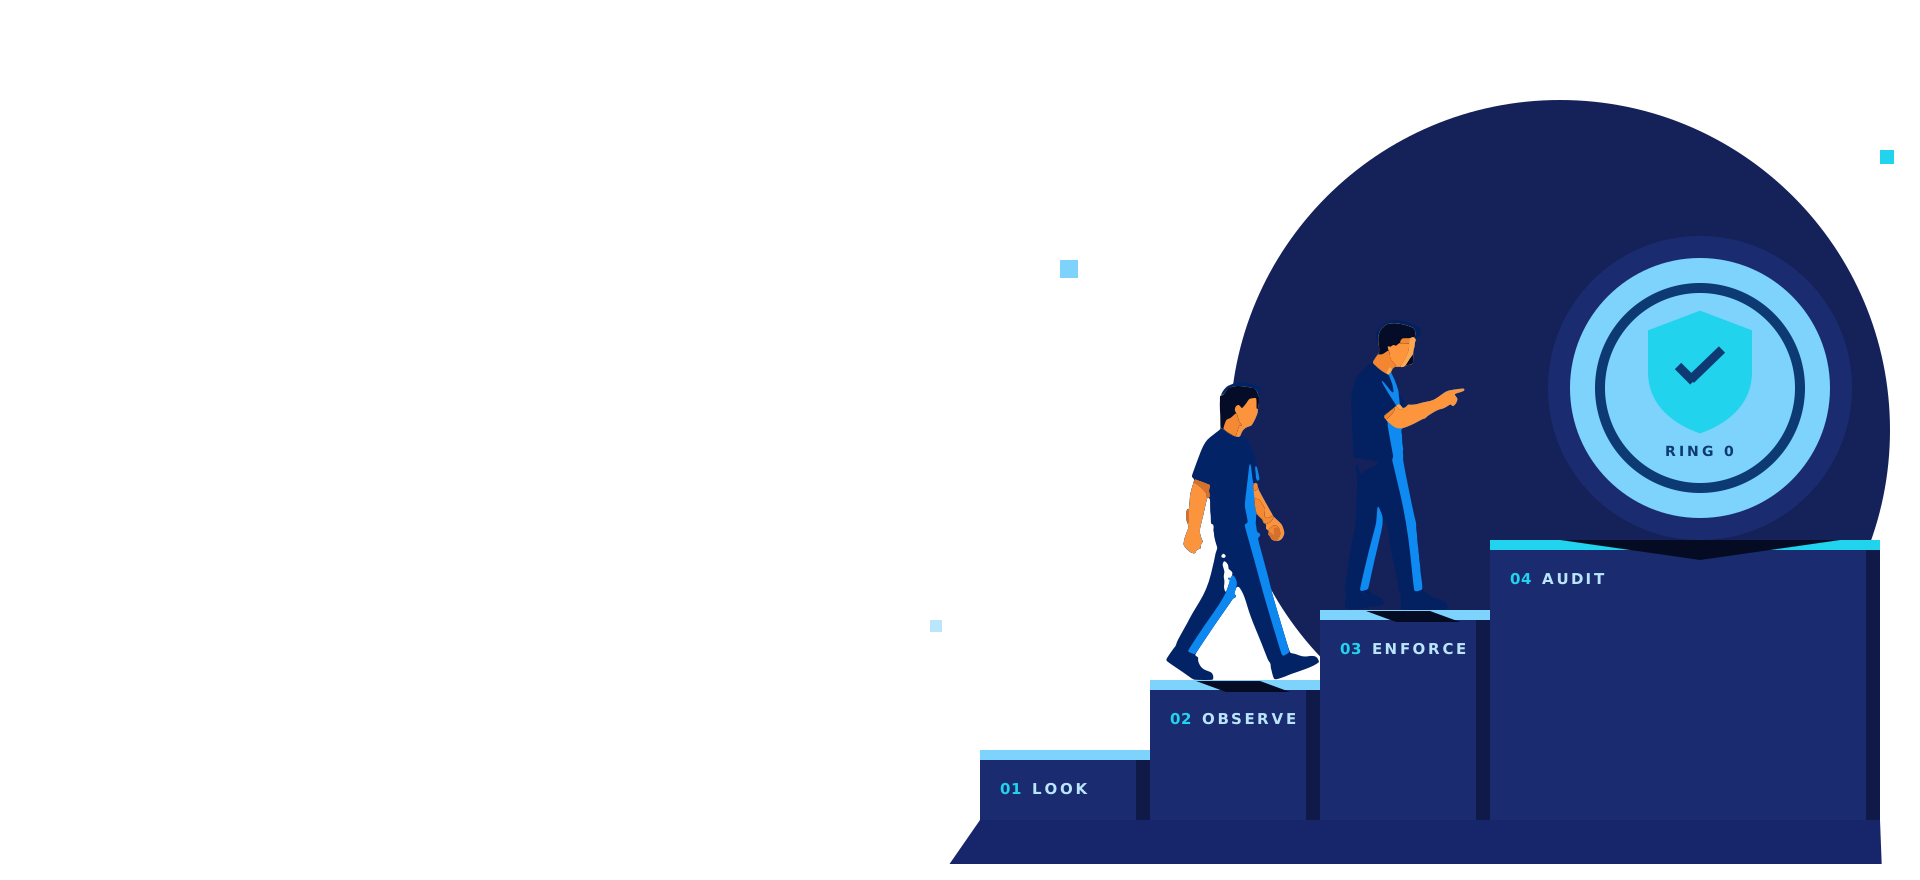
Method
We removed the attack path instead of getting better at spotting it.
Detection rate is the wrong number to optimise. Here’s why.
Signatures and models only catch what resembles something already seen. A novel intrusion doesn’t.
An unpublished exploit still can’t reach a kernel it has no route to.
Built and hosted in India — or run entirely on your own hardware.
The sequence matters more than the engine.
We map your estate first — including what can’t be patched or restarted.
The driver reports what it would block, without blocking — so nothing breaks.
Enforcement rises group by group; refused rules are logged as findings.
Daily work becomes reading containment logs, not triaging alerts.
Questions worth asking before a trial.
Isolation doesn’t stop phishing — the browser layer and credential monitoring do.
A device that stops reporting isn’t shown as safe.
Unlisted doesn’t mean safe — we report it as unknown.
Older agents show a gap, never a guessed result.
Next
Tell us what worries you. We’ll show where enforcement lands and what the first 90 days look like.